UGC NET Computer Science Software Engineering Previous Year Questions (PYQs)
Practise 146 Software Engineering questions asked in UGC NET Computer Science from 2018–2026. Questions cover Software process models, Requirements engineering, Software design, Software metrics and estimation, Software testing and Black box and white box testing. Every question is shown with its options and the correct answer, free to read.
Practise Software Engineering as timed sets
Focused 10-question sets with instant scoring, explanations, and weak-area analysis.
All 146 Software Engineering PYQs
Ordered newest exam first. Each question links back to the full paper it came from.
Question 1
UGC NET June 2026Which document outlines the functional and non-functional requirements of a software system?
- ASRS document
- BDesign document
- CTest plan
- DUser manual
Answer: (A) SRS document
Explanation
Sign in to read the full explanationQuestion 2
UGC NET June 2026Which is not a concern during the management of a software project?
- AProject/product information
- BProduct quality
- CTime
- DMoney
Answer: (B) Product quality
Explanation
Sign in to read the full explanationQuestion 3
UGC NET June 2026Match List-I with List-II.
List-I: Process model List-II: Characteristic A. Classical waterfall model
B. Prototype model
C. Evolutionary model
D. Spiral modelI. Risk analysis
II. Large problem with incremental delivery
III. Clear requirements
IV. Requirements are not well understood- AA-I, B-III, C-II, D-IV
- BA-III, B-IV, C-II, D-I
- CA-II, B-III, C-IV, D-I
- DA-IV, B-I, C-III, D-II
Answer: (B) A-III, B-IV, C-II, D-I
Explanation
Sign in to read the full explanationQuestion 4
UGC NET June 2026Match List-I with List-II.
A. Waterfall model
B. Agile methodology
C. Test-driven development
D. Continuous integrationList-I List-II A. Waterfall
B. Agile
C. TDD
D. CII. Collaboration/release feedback
II. Automated integration
III. Fixed sequential steps
IV. Tests before code- AA-III, B-I, C-II, D-IV
- BA-II, B-I, C-IV, D-II
- CA-I, B-III, C-II, D-IV
- DA-III, B-I, C-IV, D-II
Answer: (D) A-III, B-I, C-IV, D-II
Explanation
Sign in to read the full explanationQuestion 5
UGC NET June 2026A program takes 100 man-days to write in FORTRAN. Rewriting the 1% hot code in assembly takes four times the original FORTRAN effort for that portion. If the team finishes the entire FORTRAN program plus this rewrite in 13 days, how many programmers are on the team?
- A13 programmers
- B10 programmers
- C8 programmers
- D100/13 programmers
Answer: (C) 8 programmers
Explanation
Sign in to read the full explanationQuestion 6
UGC NET June 2026If 99% of the program is written in FORTRAN and 1% directly in assembly, what is the percentage increase in programming time compared with writing all FORTRAN first and then rewriting the 1% in assembly?
- A10%
- B5%
- C13%
- D8%
Answer: (B) 5%
Explanation
Sign in to read the full explanationQuestion 7
UGC NET June 2026How many days will two programmers take to write the whole program in FORTRAN and then rewrite the 1% hot code in assembly language?
- A52
- B53
- C54
- D55
Answer: (A) 52
Explanation
Sign in to read the full explanationQuestion 8
UGC NET June 2026If 99% of the program is written in FORTRAN and 1% in assembly, what is the percentage increase in execution time compared with writing the whole program in FORTRAN and then rewriting the 1% in assembly?
- A0.9%
- B1%
- C0.1%
- D0%
Answer: (D) 0%
Explanation
Sign in to read the full explanationQuestion 9
UGC NET January 2026Match List-I (Process/lifecycle models) with List-II.
List-I List-II A. V-Model I. Trigger transition B. Incremental process model II. Classic life cycle C. Spiral Model III. Risk Driven D. Concurrent Model IV. Core product - AA-IV, B-I, C-III, D-II
- BA-II, B-III, C-IV, D-I
- CA-II, B-I, C-III, D-IV
- DA-II, B-IV, C-III, D-I
Answer: (D) A-II, B-IV, C-III, D-I
Explanation
Sign in to read the full explanationQuestion 10
UGC NET January 2026Given below are two statements: one is labelled as Assertion A and the other is labelled as Reason R
Assertion (A): Higher cyclomatic complexity indicates a more complex program.
Reason (R): It is calculated based on the number of independent execution paths in the program.- ABoth A and R are correct and R is the correct explanation of A
- BBoth A and R are correct but R is NOT the correct explanation of A
- CA is correct but R is not correct
- DA is not correct but R is correct
Answer: (A) Both A and R are correct and R is the correct explanation of A
Explanation
Sign in to read the full explanationQuestion 11
UGC NET January 2026Match List-I (UML diagram types) with List-II.
LIST-I LIST-II A. Class diagram I. subset B. Package diagram II. relationship C. Object diagram III. dependencies D. Component diagram IV. static structure - AA-II, B-III, C-IV, D-I
- BA-IV, B-I, C-III, D-II
- CA-IV, B-I, C-II, D-III
- DA-III, B-IV, C-II, D-I
Answer: (C) A-IV, B-I, C-II, D-III
Explanation
Sign in to read the full explanationQuestion 12
UGC NET January 2026Arrange the following WebApp design layers from top to bottom.
A. Navigation Design
B. Aesthetic Design
C. Interface Design
D. Content Design
E. Performance Design- AC, B, D, A, E
- BC, B, D, E, A
- CC, D, B, A, E
- DC, D, A, B, E
Answer: (A) C, B, D, A, E
Explanation
Sign in to read the full explanationQuestion 13
UGC NET January 2026Which of the following statements are correct regarding task elaboration in interface design?
A. Alpha testing is done at the developer's site in a controlled environment.
B. Beta testing is done at the end-user site with developer presence.
C. Acceptance testing may be very formal and last for weeks.
D. Alpha testing always replaces Beta testing.- AA, B, C Only
- BA, B, D Only
- CB, C, D only
- DA, B, C, D
Answer: (A) A, B, C Only
Explanation
Sign in to read the full explanationQuestion 14
UGC NET January 2026Match List-I (Coupling types) with List-II.
List-I List-II A. Content coupling I. Modifies internal data of another component B. Control Coupling II. Pass control flag to influence logic C. Stamp Coupling III. Uses entire structure/class as argument D. Data Coupling IV. Passes long list of data arguments. - AA-I, B-II, C-IV, D-III
- BA-II, B-IV, C-I, D-III
- CA-I, B-III, C-IV, D-II
- DA-I, B-II, C-III, D-IV
Answer: (D) A-I, B-II, C-III, D-IV
Explanation
Sign in to read the full explanationQuestion 15
UGC NET January 2026Based on the passage, including the 10% contingency margin, what is the project cost?
A project is planned for an enterprise accounting system with an estimated size of 60 KLOC. The organization applies Basic COCOMO in Semi-Detached mode, using these parameters:
- Effort = 3.0 x (KLOC)^1.0 person-months
- Development time = 2.5 x (Effort)^0.5 months
- Average cost per person-month (PM) = $10,000
- A contingency margin of 10% on effort is mandatory
- The client demands a detailed schedule if staff is capped at 15 engineers
- A$ 1.80 M
- B$ 1.98 M
- C$ 2.4 M
- D$ 2.36 M
Answer: (B) $ 1.98 M
Explanation
Sign in to read the full explanationQuestion 16
UGC NET January 2026Based on the passage, what is the estimated development time in months?
A project is planned for an enterprise accounting system with an estimated size of 60 KLOC. The organization applies Basic COCOMO in Semi-Detached mode, using these parameters:
- Effort = 3.0 x (KLOC)^1.0 person-months
- Development time = 2.5 x (Effort)^0.5 months
- Average cost per person-month (PM) = $10,000
- A contingency margin of 10% on effort is mandatory
- The client demands a detailed schedule if staff is capped at 15 engineers
- A28 Months
- B26 Months
- C34 Months
- D12 Months
Answer: (C) 34 Months
Explanation
Sign in to read the full explanationQuestion 17
UGC NET January 2026Based on the passage, what is the implied average staffing level?
A project is planned for an enterprise accounting system with an estimated size of 60 KLOC. The organization applies Basic COCOMO in Semi-Detached mode, using these parameters:
- Effort = 3.0 x (KLOC)^1.0 person-months
- Development time = 2.5 x (Effort)^0.5 months
- Average cost per person-month (PM) = $10,000
- A contingency margin of 10% on effort is mandatory
- The client demands a detailed schedule if staff is capped at 15 engineers
- A8 Engineers
- B5 Engineers
- C10 Engineers
- D12 Engineers
Answer: (B) 5 Engineers
Explanation
Sign in to read the full explanationQuestion 18
UGC NET January 2026Based on the passage, if the staff is capped at 15 engineers, what is the revised calendar duration?
A project is planned for an enterprise accounting system with an estimated size of 60 KLOC. The organization applies Basic COCOMO in Semi-Detached mode, using these parameters:
- Effort = 3.0 x (KLOC)^1.0 person-months
- Development time = 2.5 x (Effort)^0.5 months
- Average cost per person-month (PM) = $10,000
- A contingency margin of 10% on effort is mandatory
- The client demands a detailed schedule if staff is capped at 15 engineers
- A20.0 Months
- B18.4 Months
- C13.2 Months
- D22.0 Months
Answer: (C) 13.2 Months
Explanation
Sign in to read the full explanationQuestion 19
UGC NET January 2026Based on the passage, what is the initial effort, in person-months (PM), before adding the contingency margin?
A project is planned for an enterprise accounting system with an estimated size of 60 KLOC. The organization applies Basic COCOMO in Semi-Detached mode, using these parameters:
- Effort = 3.0 x (KLOC)^1.0 person-months
- Development time = 2.5 x (Effort)^0.5 months
- Average cost per person-month (PM) = $10,000
- A contingency margin of 10% on effort is mandatory
- The client demands a detailed schedule if staff is capped at 15 engineers
- A240 PM
- B260 PM
- C180 PM
- D200 PM
Answer: (C) 180 PM
Explanation
Sign in to read the full explanationQuestion 20
UGC NET June 2025Which is not a requirements-elicitation technique?
- AInterviews
- BThe use-case approach
- CFacilitated Application Specification Technique (FAST)
- DData-flow diagram
Answer: (D) Data-flow diagram
Explanation
Sign in to read the full explanationQuestion 21
UGC NET June 2025In basic COCOMO, the effort estimate for organic software is:
- AE = 2.4(KLOC)^1.05 person-months
- BE = 3.4(KLOC)^1.06 person-months
- CE = 2.0(KLOC)^1.05 person-months
- DE = 2.4(KLOC)^1.07 person-months
Answer: (A) E = 2.4(KLOC)^1.05 person-months
Explanation
Sign in to read the full explanationQuestion 22
UGC NET June 2025The process used to discover difficult, unknown, and hidden information about an existing software system is called:
- ASoftware engineering
- BSoftware re-engineering
- CReverse engineering
- DInverse engineering
Answer: (C) Reverse engineering
Explanation
Sign in to read the full explanationQuestion 23
UGC NET June 2025Which is not a software characteristic?
- ASoftware does not wear out.
- BSoftware is flexible.
- CSoftware is not manufactured.
- DSoftware is always correct.
Answer: (D) Software is always correct.
Explanation
Sign in to read the full explanationQuestion 24
UGC NET June 2025Arrange stamp coupling, control coupling, external coupling, common coupling, and content coupling from lowest to highest coupling.
- AE, A, C, B, D
- BD, B, A, E, C
- CB, C, D, A, E
- DC, A, B, D, E
Answer: (C) B, C, D, A, E
Explanation
Sign in to read the full explanationQuestion 25
UGC NET June 2025Arrange unit, integration, system, and acceptance testing in their usual software-development order.
- AB, C, A, D
- BB, A, C, D
- CC, B, A, D
- DC, B, D, A
Answer: (B) B, A, C, D
Explanation
Sign in to read the full explanation- Practise Software Engineering in a timed set
Question 26
UGC NET June 2025Which cohesions are better than procedural cohesion?
- AFunctional and communicational only
- BFunctional, sequential, and communicational only
- CTemporal, communicational, and logical only
- DFunctional, communicational, and logical only
Answer: (B) Functional, sequential, and communicational only
Explanation
Sign in to read the full explanationQuestion 27
UGC NET June 2025Which are McCall quality factors: maintainability, usability, integrity, and functionality?
- AA and D only
- BA, B, and D only
- CC and D only
- DA, B, and C only
Answer: (D) A, B, and C only
Explanation
Sign in to read the full explanationQuestion 28
UGC NET June 2025Match reliability, efficiency, maintainability, and portability with their software-quality descriptions.
Characteristic Description A. Reliability I. Transfer between environments B. Efficiency II. Sustained performance over time C. Maintainability III. Performance relative to resources D. Portability IV. Effort needed for modification - AA-II, B-III, C-I, D-IV
- BA-II, B-III, C-IV, D-I
- CA-III, B-II, C-I, D-IV
- DA-IV, B-II, C-I, D-III
Answer: (B) A-II, B-III, C-IV, D-I
Explanation
Sign in to read the full explanationQuestion 29
UGC NET June 2025Match equivalence partitioning, boundary-value analysis, cyclomatic complexity, and decision-table testing with their testing focus.
Technique Focus A. Equivalence Partitioning I. Independent code paths B. Boundary Value Analysis II. Valid/invalid input sets C. Cyclomatic Complexity III. Input-range limits D. Decision Table Testing IV. Action combinations and conditions - AA-II, B-III, C-I, D-IV
- BA-II, B-III, C-IV, D-I
- CA-III, B-II, C-I, D-IV
- DA-IV, B-II, C-I, D-III
Answer: (A) A-II, B-III, C-I, D-IV
Explanation
Sign in to read the full explanationQuestion 30
UGC NET January 2025As per the Software Engineering Institute, identify the correct maturity sequence:
A. Initial
B. Repeatable
C. Managed
D. Optimizing
E. Defined- AA, B, C, D, E
- BA, B, E, C, D
- CA, E, C, D, B
- DA, E, B, C, D
Answer: (B) A, B, E, C, D
Explanation
Sign in to read the full explanationQuestion 31
UGC NET January 2025The characteristics of modern programming are:
A. Each module should do only one thing.
B. Communication between modules is allowed only through a calling module.
C. Communication can take place directly between modules without a calling-called relationship.
D. Modules are single-entry, single-exit systems using control structures.- AA, B and C only
- BA, B and D only
- CA, C and D only
- DC and D only
Answer: (B) A, B and D only
Explanation
Sign in to read the full explanationQuestion 32
UGC NET January 2025Find the correct sequence of the prototype software-development model.
A. Start
B. Develop prototype
C. Deliver to customer
D. Quick design
E. Quick play- AA, B, C, D, E
- BA, E, D, B, C
- CA, B, D, E, C
- DA, B, E, D, C
Answer: (B) A, E, D, B, C
Explanation
Sign in to read the full explanationQuestion 33
UGC NET January 2025Software testability is how easily software can be tested. Which characteristic does not lead to testable software?
- AObservability
- BControllability
- CRepairability
- DUnderstandability
Answer: (C) Repairability
Explanation
Sign in to read the full explanationQuestion 34
UGC NET January 2025Which one of the following is the correct estimation model based on the software equation?
- AE = [LOC × B⁰·²²² / P]² × (1/t⁴)
- BE = [LOC × B⁰·³³³ / P]³ × (1/t⁴)
- CE = [LOC × B⁰·⁴⁴⁴ / P]⁴ × (1/t³)
- DE = [LOC × B⁰·¹¹¹ / P]⁶ × (1/t³)
Answer: (B) E = [LOC × B⁰·³³³ / P]³ × (1/t⁴)
Explanation
Sign in to read the full explanationQuestion 35
UGC NET January 2025In Software Engineering, Jackson’s Principles are based on:
A. Designation
B. Definitions
C. Refutable assertions
D. Formal review
E. Requirement elicitation- AA, B and C only
- BB, C and D only
- CC, D and E only
- DB, C and D only
Answer: (A) A, B and C only
Explanation
Sign in to read the full explanationQuestion 36
UGC NET January 2025Collaborative document inspection technique is used for
- ARequirement validation process
- BRequirement verification process
- CIntegration testing
- DBlack-box testing
Answer: (A) Requirement validation process
Explanation
Sign in to read the full explanationQuestion 37
UGC NET January 2025Which one of the following is not part of requirement management?
- AFeatures Traceability Table
- BDependency Traceability Table
- CInterface Traceability Table
- DPage Traceability Table
Answer: (D) Page Traceability Table
Explanation
Sign in to read the full explanationQuestion 38
UGC NET January 2025Identify the correct statements regarding the spiral model.
A. Spiral model is an incremental process model.
B. Spiral model is a risk-driven process model.
C. Spiral model is an acyclic balancing approach.
D. Spiral model involves a set of anchor-point milestones.- AA and B only
- BB and C only
- CA and D only
- DB and D only
Answer: (D) B and D only
Explanation
Sign in to read the full explanationQuestion 39
UGC NET January 2025Match List-I with List-II.
List-I: software risk List-II: uses A. Predictable risk
B. Business risk
C. Project risk
D. Past projectI. Strategic risk
II. Staffing and organization
III. Implementation
IV. Past-project experience- AA-IV, B-III, C-I, D-II
- BA-III, B-II, C-I, D-IV
- CA-I, B-IV, C-III, D-II
- DA-IV, B-I, C-II, D-III
Answer: (D) A-IV, B-I, C-II, D-III
Explanation
Sign in to read the full explanationQuestion 40
UGC NET August 2024Arrange the following steps of Feature Drive
Development (FDD) process in the correct
sequence :
A. Develop an overall model
B. Build by feature
C. Plan by feature
D. Design by feature
E. Build a feature list- A(A), (C), (B), (E), (D)
- B(A), (E), (C), (D), (B)
- C(B),(A),(D),(E),(C)
- D(A), (B), (C), (E), (D)
Answer: (B) (A), (E), (C), (D), (B)
Explanation
Sign in to read the full explanationQuestion 41
UGC NET August 2024Which of the following are Agile Process Models
?
A. Extreme Programming (XP)
B. Waterfall
C. Scrum
D. Spiral
E. Incremental- A(A) and (C) Only
- B(B) and (C) Only
- C(A) and (D) Only
- D(B) and (E) Only
Answer: (A) (A) and (C) Only
Explanation
Sign in to read the full explanationQuestion 42
UGC NET August 2024Arrange the following phases of the Agile
process in the correct sequence :
A. Design
B. Release
C. Testing
D. Development
E. Planning- A(A), (B), (D), (E), (C)
- B(A), (D), (E), (B), (C)
- C(E), (A), (D), (C), (B)
- D(E), (D), (A), (C), (B)
Answer: (C) (E), (A), (D), (C), (B)
Explanation
Sign in to read the full explanationQuestion 43
UGC NET August 2024If a software project has 2000 lines of code
(LOC) and the average productivity rate is 10
LOC per person-hour, how many person-hours
are required to complete the project?- A100
- B150
- C200
- D250
Answer: (C) 200
Explanation
Sign in to read the full explanationQuestion 44
UGC NET August 2024Which of the following are typical activities in the
software process lifecycle?
A. Requirement Analysis
B. System Design
C. Code Refactoring
D. Deployment
E. Substructure- A(A), (B), (C) Only
- B(B), (C), (D) Only
- C(A), (B), (D) Only
- D(A), (D), (E) Only
Answer: (C) (A), (B), (D) Only
Explanation
Sign in to read the full explanationQuestion 45
UGC NET August 2024Match List-I with List-II.
List-I (software design principles) List-II (Definition) (A) Cohesion (I) Degree to which one module relies on another module. (B) Coupling (II) Dividing a software system into distinct modules. (C) Abstraction (III) Degree to which elements of a module belong together. (D) Modularity (IV) Simplifying complex reality by modeling classes appropriate to the problem. - A(A)-(I), (B)-(II), (C)-(III), (D)-(IV)
- B(A)-(II), (B)-(III), (C)-(IV), (D)-(I)
- C(A)-(III), (B)-(I), (C)-(IV), (D)-(II)
- D(A)-(III), (B)-(IV), (C)-(II), (D)-(I)
Answer: (C) (A)-(III), (B)-(I), (C)-(IV), (D)-(II)
Explanation
Sign in to read the full explanationQuestion 46
UGC NET August 2024Given a project with an estimated effort of 1500
person-hours and a team of 5 people, how many
days will it take to complete the project, if each
person works 8 hours a day?- A30
- B37.5
- C40
- D45.5
Answer: (B) 37.5
Explanation
Sign in to read the full explanationQuestion 47
UGC NET August 2024In Software configuration management, what is
the primary purpose of version control ?- ATo control the changes made to software
- BTo document user requirements
- CTo estimate project cost
- DTo design the software architecture
Answer: (A) To control the changes made to software
Explanation
Sign in to read the full explanationQuestion 48
UGC NET August 2024Match List-I with List-II.
List-I (Testing Type) List-II (Description) (A) Unit testing (I) Testing individual components of the software. (B) Integration testing (II) Testing the interaction between integrated components. (C) System testing (III) Testing to verify the system meets business needs. (D) Acceptance testing (IV) Testing the complete system to ensure it meets requirements. - A(A)-(I), (B)-(II), (C)-(III), (D)-(IV)
- B(A)-(I), (B)-(II), (C)-(IV), (D)-(III)
- C(A)-(I), (B)-(III), (C)-(II), (D)-(IV)
- D(A)-(I), (B)-(IV), (C)-(II), (D)-(III)
Answer: (B) (A)-(I), (B)-(II), (C)-(IV), (D)-(III)
Explanation
Sign in to read the full explanationQuestion 49
UGC NET August 2024Given a project that uses the COCOMO model
with an estimated effort of 2000 person-months
and a productivity rate of 5 person-month per
KLOC, what is the estimated size of the project in
KLOC ?- A200
- B400
- C100
- D50
Answer: (B) 400
Explanation
Sign in to read the full explanationQuestion 50
UGC NET December 2023Test suite is consist of :
- ASet of defect cases
- BSet of boundary cases
- CSet of test cases
- DSet of nest cases
Answer: (C) Set of test cases
Explanation
Sign in to read the full explanation- Practise Software Engineering in a timed set
Question 51
UGC NET December 2023Level - 0 DFD is also called as :
- AUse case Diagram
- BSequence Diagram
- CContext Diagram
- DPrototype Diagram
Answer: (C) Context Diagram
Explanation
Sign in to read the full explanationQuestion 52
UGC NET December 2023The selection of Spiral Model based on characteristics of requirements :
A. Are requirements easily understandable and defined ?
B. Do we change requirements quite often ?
C. Can we define requirements early in the cycle ?
D. Requirements are indicating a complex to be built Choose the correct answer from the options given below : @) © Only- AC only
- BB only
- CB and D only
- DA and C only
Answer: (C) B and D only
Explanation
Sign in to read the full explanationQuestion 53
UGC NET December 2023Evaluate these statements: Statement I: The friend function and the member functions of a friend class directly access the private and protected data. Statement II: The friend function can access the private data through the member functions of the base class In the light of the above statements, choose the most appropriate answer from the options given below :
- ABoth Statement I and Statement II are correct
- BBoth Statement I and Statement II are incorrect
- CStatement I is correct but Statement II is incorrect
- DStatement I is incorrect but Statement II is correct
Answer: (A) Both Statement I and Statement II are correct
Explanation
Sign in to read the full explanationQuestion 54
UGC NET December 2023Which of the following join is used to get all the tuples of relation X and Y with Null values of corresponding missing values ?
X (S, Si, C) Y (S, P, D) (J, 1, M)
(B, 2, N)
(R, 3, H)
(T, 4, G)
(J, S₁, CA)
(B, P₁, AB)
(R, D₁, DC)
(A, H₁, MD)
- ALeft outer join
- BRight outer join
- CNatural join
- DFull outer join
Answer: (D) Full outer join
Explanation
Sign in to read the full explanationQuestion 55
UGC NET June 2023A software system experienced five failures during testing. The time elapsed since the previous failure, in hours, is shown in the table.
Error number 1 2 3 4 5 Time since last failure (hours) 6 4 8 5 6 Using the exponential reliability model with the failure rate estimated from the mean time between these five failures, what is the reliability of the software running for the next one hour without failing?
- Ae^(−9/29)
- Be^(−7/29)
- Ce^(−5/29)
- De^(−3/29)
Answer: (C) e^(−5/29)
Explanation
Sign in to read the full explanationQuestion 56
UGC NET June 2023Which of the following is used to determine cost performance index?
- ABudgeted cost work performed - budget at completion
- BBudgeted cost work performed ÷ budget at completion
- CBudgeted cost work performed ÷ Actual cost work performed
- DBudgeted cost work performed - Actual cost work performed
Answer: (C) Budgeted cost work performed ÷ Actual cost work performed
Explanation
Sign in to read the full explanationQuestion 57
UGC NET June 2023Statement I: At the interaction level, components provide an operator display interface and an interface with the communication system used.
Statement II: At the I/O management level, components handle operator authentication, report generator and query manager.- ABoth Statement I and Statement II are correct
- BBoth Statement I and Statement II are incorrect
- CStatement I is correct but Statement II is incorrect
- DStatement I is incorrect but Statement II is correct
Answer: (C) Statement I is correct but Statement II is incorrect
Explanation
Sign in to read the full explanationQuestion 58
UGC NET June 2023Assertion (A): Validity checks real need of system users.
Reason (R): Completeness checks system user defined requirements.- ABoth A and R are true and R is the correct explanation of A
- BBoth A and R are true but R is NOT the correct explanation of A
- CA is true but R is false
- DA is false but R is true
Answer: (B) Both A and R are true but R is NOT the correct explanation of A
Explanation
Sign in to read the full explanationQuestion 59
UGC NET June 2023Statement I: subsystem models show logical grouping of objects into coherent subsystem.
Statement II: State machine models show how objects change their states in response to events.- ABoth Statement I and Statement II are correct
- BBoth Statement I and Statement II are incorrect
- CStatement I is correct but Statement II is incorrect
- DStatement I is incorrect but Statement II is correct
Answer: (A) Both Statement I and Statement II are correct
Explanation
Sign in to read the full explanationQuestion 60
UGC NET June 2023Consider the following statements:
A. Dynamic metrics are collected by measurements made of a program in execution
B. Static metrics are collected by measurements made of representations of the system
C. The assessment of software quality is an objective process
D. An important part of quality assurance in the selection of standards that should apply to the software development process.- AA, B, C only
- BB, C and D only
- CA, C and D only
- DA, B and D only
Answer: (D) A, B and D only
Explanation
Sign in to read the full explanationQuestion 61
UGC NET June 2023___________ is intended to show that a system both conforms to its specifications and meets the expectations of the system customer.
- ASoftware specification
- BSoftware design
- CSoftware evaluation
- Dsoftware validation
Answer: (D) software validation
Explanation
Sign in to read the full explanationQuestion 62
UGC NET June 2023An observational technique that can be used to understand operational process and help to derive requirement for software to support operational process is known as
- ARequirement specification
- BStructural specification
- CEthnography
- DNatural language specification
Answer: (C) Ethnography
Explanation
Sign in to read the full explanationQuestion 63
UGC NET June 2023Match List I with List II on PERT and CPM concepts.
List-I List-II A. PERT I. used for non repetitive jobs B. Optimistic time II. Used for repetitive jobs C. CPM III. The shortest possible time to complete the activity if all goes well D. Pessimistic time IV. The longest time that an activity takes List I / List II: PERT and CPM project management concepts
- AA-III, B-IV, C-II, D-I
- BA-IV, B-I, C-II, D-III
- CA-I, B-III, C-II, D-II
- DA-I, B-III, C-II, D-IV
Answer: (D) A-I, B-III, C-II, D-IV
Explanation
Sign in to read the full explanationQuestion 64
UGC NET June 2023Match List I with List II on software testing types.
List-I List-II A. Scenario testing I. To verify the I/O behavior of a test object B. Regression testing II. User acceptance methodology C. Component testing III. No new bugs after changes in the program D. Beta testing IV. The documentation of a use case Software testing types with their definitions
- AA-IV, B-III, C-II, D-I
- BA-II, B-I, C-III, D-IV
- CA-IV, B-III, C-I, D-II
- DA-III, B-I, C-IV, D-II
Answer: (C) A-IV, B-III, C-I, D-II
Explanation
Sign in to read the full explanationQuestion 65
UGC NET March 2023Which of the following is not a Non functional requirement?
- APortability
- BSecurity
- CScalability
- DUser interaction
Answer: (D) User interaction
Explanation
Sign in to read the full explanationQuestion 66
UGC NET March 2023COCOMO stands for ______
- AConsumed cost model
- BConstructive cost model
- CCommon control model
- DComposition cost model
Answer: (B) Constructive cost model
Explanation
Sign in to read the full explanationQuestion 67
UGC NET March 2023Modifying the software to match changes in the ever changing environment is called as
- AAdaptive maintenance
- BCorrective maintenance
- CPerfective maintenance
- DPreventive maintenance
Answer: (A) Adaptive maintenance
Explanation
Sign in to read the full explanationQuestion 68
UGC NET March 2023For a function of two variables, boundary value analysis yields,
- A4n+3 test cases
- B4n+1 test cases
- Cn+4 test cases
- D2n+4 test cases
Answer: (B) 4n+1 test cases
Explanation
Sign in to read the full explanationQuestion 69
UGC NET March 2023How do you create agile processes to manage unpredictability?
A. Requirements gathering must be conducted very carefully.
B. Risk analysis must be conducted before planning takes place.
C. Software increments must be delivered in short time periods.
D. Software processes must not adapt to changes incrementally.Choose the correct answer from the options given below:
- AA only
- BB only
- CC only
- DD only
Answer: (C) C only
Explanation
Sign in to read the full explanationQuestion 70
UGC NET March 2023Software project manager is responsible for the following tasks:
A. Project Planning
B. Project status tracking
C. Resource management
D. Risk management
E. Project delivery within time & budget.Choose the correct answer from the options given below:
- AAll the statements are correct.
- BOnly B & C are correct.
- COnly A & D are correct
- DAll the statements are not correct.
Answer: (A) All the statements are correct.
Explanation
Sign in to read the full explanationQuestion 71
UGC NET March 2023Mr. X designed open source software which must comply with some criteria. Choose the false statement in respect of above.
A. No restriction on redistribution of the software as part or whole.
B. The integrity of the author's source code must be maintained.
C. The software can be sold after distribution.Choose the correct answer from the options given below:
- AA only
- BB only
- CC only
- DAll statements are false
Answer: (C) C only
Explanation
Sign in to read the full explanationQuestion 72
UGC NET March 2023Match List I with List II.
List-I List-II A. Product complexity I. System Requirements Design B. Structured System analysis II. Software design C. Coupling & Cohesion III. Validation techniques D. Symbolic Execution IV. Software cost estimation List I and List II for the matching question
- AA-II, B-III, C-IV, D-I
- BA-III, B-I, C-IV, D-II
- CA-IV, B-I, C-II, D-III
- DA-III, B-IV, C-I, D-II
Answer: (C) A-IV, B-I, C-II, D-III
Explanation
Sign in to read the full explanationQuestion 73
UGC NET March 2023Consider the statements:
A. There does not exist a polynomial time algorithm to solve integer linear programming problem.
B. Main focus of PERT is 'minimizing time'.Choose the correct option about the statements A and B.
- AA is True; B is True
- BA is True; B is False
- CA is False; B is True
- DA is False; B is False
Answer: (A) A is True; B is True
Explanation
Sign in to read the full explanationQuestion 74
UGC NET March 2023Given below are two statements, one is labeled as Assertion A and the other is labelled as Reason R.
Assertion (A): Cohesion is a qualitative indication of the degree to which a module can be written more compactly and is able to complete its function in a timely manner.
Reason (R): Cohesion is a qualitative indication of the degree to which a module is connected to other modules and the outside world.
In the light of the above statements, choose the most appropriate answer from the options given below.
- ABoth A and R are correct and R is the correct explanation of A.
- BBoth A and R are correct but R is NOT the correct explanation of A.
- CA is correct but R is not correct.
- DA is not correct but R is correct.
Answer: (C) A is correct but R is not correct.
Explanation
Sign in to read the full explanationQuestion 75
UGC NET March 2023Which of the following is not one of the principles of good coding?
- ACreate unit tests before you begin coding.
- BCreate visual layout that aids understanding.
- CRefractor the code after you completes the first coding pass.
- DWrite self-documenting code not program documentation.
Answer: (D) Write self-documenting code not program documentation.
Explanation
Sign in to read the full explanation- Practise Software Engineering in a timed set
Question 76
UGC NET March 2023If P is the risk probability, L is the loss, then Risk exposure (RE) is computed as ____.
- ARE = P/L
- BRE = P+L
- CRE = P*L
- DRE = 2+(P*L)
Answer: (C) RE = P*L
Explanation
Sign in to read the full explanationQuestion 77
UGC NET March 2023Which of the following is a technique used for component wrapping?
- ABlack-box wrapping
- BClear-box wrapping
- CGray-box wrapping
- DWhite-box wrapping
Answer: (A) Black-box wrapping
Explanation
Sign in to read the full explanationQuestion 78
UGC NET March 2023The cyclomatic complexity metric provides the designer with information regarding the number of __________.
- ACycles in the program
- BErrors in the program
- CIndependent logic paths in the program
- DStatements in the program
Answer: (C) Independent logic paths in the program
Explanation
Sign in to read the full explanationQuestion 79
UGC NET March 2023Given below are two statements:
Statement I: Software testing must be recognized as a significant effort, and its planning must begin at the earliest possible time.
Statement II: The cost of software testing is an important contribution in determining overall software development costs.
In the light of the above statements, choose the correct answer from the options given below
- ABoth Statement I and Statement II are true.
- BBoth Statement I and Statement II are false.
- CStatement I is true but Statement II is false.
- DStatement I is false but Statement II is true.
Answer: (A) Both Statement I and Statement II are true.
Explanation
Sign in to read the full explanationQuestion 80
UGC NET March 2023Which of the following need not be assessed during unit testing?
A. Algorithmic performance
B. Number of lines of code
C. Error handling
D. Execution pathsChoose the correct answer from the options given below:
- AA, B, C only
- BA, B, D only
- CA, C, D only
- DB, C, D only
Answer: (B) A, B, D only
Explanation
Sign in to read the full explanationQuestion 81
UGC NET March 2023Match List I with List II.
List-I List-II A. Condition coverage I. Black box testing B. Equivalence class Partitioning II. System testing C. Volume testing III. White box testing D. Alpha testing IV. Performance testing - AA-II, B-III, C-IV, D-I
- BA-III, B-I, C-IV, D-II
- CA-IV, B-I, C-II, D-III
- DA-III, B-IV, C-I, D-II
Answer: (D) A-III, B-IV, C-I, D-II
Explanation
Sign in to read the full explanationQuestion 82
UGC NET March 2023The incremental model of software development is__________.
- AA reasonable approach when requirements are well defined.
- BA good approach when a working core product is required quickly.
- CThe best approach to use for projects with large development teams.
- DA revolutionary model that is not used for commercial products.
Answer: (B) A good approach when a working core product is required quickly.
Explanation
Sign in to read the full explanationQuestion 83
UGC NET March 2023The primary objectives of the SWE-IPT are to:
A. Solicit stakeholder needs and expectations.
B. Specify the software requirements for the product and post-development processes.
C. Generate the integrated technical plans for accomplishing the software development effort.
D. Translate stakeholder requirements into a complete, specified architectural description.
E. Ensure that the software technical data package is sufficiently detailed to facilitate an efficient and effective software implementation.Choose the correct answer from the options given below:
- AAll the statements are correct.
- BOnly B & C are correct.
- COnly A & E are correct.
- DOnly C, D & E are correct.
Answer: (A) All the statements are correct.
Explanation
Sign in to read the full explanationQuestion 84
UGC NET October 2022RAD software process model stands for
- ARapid Application Development
- BRelative Application Development
- CRapid Application Design
- DRecent Application Development
Answer: (A) Rapid Application Development
Explanation
Sign in to read the full explanationQuestion 85
UGC NET October 2022If every requirement can be checked by a cost – effective process, then SRS is called
- AVerifiable
- BTracable
- CModifiable
- DComplete
Answer: (A) Verifiable
Explanation
Sign in to read the full explanationQuestion 86
UGC NET October 2022Fault base testing technique is
- AUnit testing
- BBeta testing
- CStress testing
- DMutation testing
Answer: (D) Mutation testing
Explanation
Sign in to read the full explanationQuestion 87
UGC NET October 2022Alpha and Beta testing are forms of
- AWhite – Box Testing
- BBlack – Box Testing
- CAcceptance Testing
- DSystem Testing
Answer: (C) Acceptance Testing
Explanation
Sign in to read the full explanationQuestion 88
UGC NET October 2022The process to gather the software requirements from client, analyze and document is known as:-
- ASoftware Engineering Process
- BUser Engineering Process
- CRequirement Elicitation Process
- DRequirement Engineering Process
Answer: (D) Requirement Engineering Process
Explanation
Sign in to read the full explanationQuestion 89
UGC NET October 2022Size and complexity are a part of
- APeople Metrics
- BProject Metrics
- CProcess Metrics
- DProduct Metrics
Answer: (D) Product Metrics
Explanation
Sign in to read the full explanationQuestion 90
UGC NET October 2022Which Metrics are derived by normalizing quality and/or productivity measures by considering the size of the software that has been produced?
- AFunction – Oriented Metrics
- BFunction – Point Metrics
- CLine of Code Metrics
- DSize Oriented Metrics
Answer: (D) Size Oriented Metrics
Explanation
Sign in to read the full explanationQuestion 91
UGC NET October 2022The model in which the requirements are implemented by its category is
- AEvolutionary Development Model
- BWaterfall Model
- CPrototyping Model
- DIterative Enhancement Model
Answer: (D) Iterative Enhancement Model
Explanation
Sign in to read the full explanationQuestion 92
UGC NET October 2022Which of the following is an indirect measure of product?
- AQuality
- BComplexity
- CReliability
- DAll of these
Answer: (D) All of these
Explanation
Sign in to read the full explanationQuestion 93
UGC NET October 2022Modules X and Y operate on the same input and output, then the cohesion is
- ALogical cohesion
- BSequential cohesion
- CProcedural cohesion
- DCommunicational cohesion
Answer: (D) Communicational cohesion
Explanation
Sign in to read the full explanationQuestion 94
UGC NET October 2022Consider the following related to Fourth Generation Technique (4GT):
A. It controls efforts.
B. It controls resources.
C. It controls cost of development.
Choose the correct answer from the options given below:- A(A) and (B) only
- B(B) and (C) only
- C(C) and (A) only
- DAll (A), (B) and (C)
Answer: (D) All (A), (B) and (C)
Explanation
Sign in to read the full explanationQuestion 95
UGC NET October 2022Match List I with List II regarding software design concepts.
List-I List-II A. Localization I. Encapsulation B. Packaging or binding of a collection of items II. Abstraction C. Mechanism that enables designer to focus on essential details of a program component III. Characteristic of software that indicates the manner in which information is concentrated in program D. Information hiding IV. Suppressing the operational details of a program component - A(A)-(I), (B)-(II), (C)-(III), (D)-(IV)
- B(A)-(II), (B)-(I), (C)-(III), (D)-(IV)
- C(A)-(III), (B)-(I), (C)-(II), (D)-(IV)
- D(A)-(III), (B)-(I), (C)-(IV), (D)-(II)
Answer: (C) (A)-(III), (B)-(I), (C)-(II), (D)-(IV)
Explanation
Sign in to read the full explanationQuestion 96
UGC NET October 2022A top down approach to programming calls for :
Statement I: Working from the general to the specific.
Statement II: Postpone the minor decisions.
Statement III: A systematic approach.
Statement IV: Intermediate coding of the problem.
Which of the following is true?- AStatement I only
- BStatement I and Statement II only
- CStatement I, Statement II and Statement III only
- DStatement I, Statement II and Statement IV only
Answer: (C) Statement I, Statement II and Statement III only
Explanation
Sign in to read the full explanationQuestion 97
UGC NET October 2022A good software requirement specification does NOT have the characteristic
- ACompleteness
- BConsistency
- CClarity
- DReliability
Answer: (D) Reliability
Explanation
Sign in to read the full explanationQuestion 98
UGC NET November 2021In software testing, beta testing is the testing performed by ______.
- Apotential customers at the developer's location
- Bpotential customers at their own locations
- Cproduct developers at the customer's location
- Dproduct developers at their own locations
Answer: (B) potential customers at their own locations
Explanation
Sign in to read the full explanationQuestion 99
UGC NET November 2021In the MVC architectural pattern, the View component is responsible for:
- AUser interface
- BSecurity of the system
- CBusiness logic and domain objects
- DTranslating between user interface actions/events and operations on the domain objects
Answer: (A) User interface
Explanation
Sign in to read the full explanationQuestion 100
UGC NET November 2021In software engineering, what kind of notation do formal methods predominantly use?
- Atextual
- Bdiagrammatic
- Cmathematical
- Dcomputer code
Answer: (C) mathematical
Explanation
Sign in to read the full explanation- Practise Software Engineering in a timed set
Question 101
UGC NET November 2021If every requirement stated in the Software Requirement Specification (SRS) has only one interpretation, then the SRS is said to be:
- Acorrect
- Bconsistent
- Cunambiguous
- Dverifiable
Answer: (C) unambiguous
Explanation
Sign in to read the full explanationQuestion 102
UGC NET November 2021A system has 99.99% uptime and a mean-time-between-failure (MTBF) of 1 day. How quickly must the system repair itself to meet this availability goal?
- A~9 seconds
- B~10 seconds
- C~11 seconds
- D~12 seconds
Answer: (A) ~9 seconds
Explanation
Sign in to read the full explanationQuestion 103
UGC NET November 2021In Software Configuration Management (SCM), which kinds of files should be committed to the source control repository?
A. Code files
B. Documentation files
C. Output files
D. Automatically generated files that are required for the system to be usedChoose the correct answer from the options given below:
- AA and B only
- BB and C only
- CC and D only
- DD and A only
Answer: (A) A and B only
Explanation
Sign in to read the full explanationQuestion 104
UGC NET November 2021Match List-I (Software Process Model) with List-II (Description).
List-I List-II A. Waterfall Model I. Software can be developed incrementally B. Evolutionary Model II. Requirement compromises are inevitable C. Component-based Software Engineering III. Explicit recognition of risk D. Spiral Development IV. Inflexible partitioning of the project into stages - AA-IV, B-I, C-III, D-II
- BA-I, B-IV, C-II, D-III
- CA-II, B-III, C-I, D-IV
- DA-IV, B-I, C-II, D-III
Answer: (D) A-IV, B-I, C-II, D-III
Explanation
Sign in to read the full explanationQuestion 105
UGC NET November 2021Identify the correct order (lower to higher) of the five levels of the Capability Maturity Model used to measure the maturity of an organisation's software process.
A. Defined
B. Optimizing
C. Initial
D. Managed
E. RepeatableChoose the correct answer from the options given below:
- AC, A, E, D, B
- BC, E, A, B, D
- CC, B, D, E, A
- DC, E, A, D, B
Answer: (D) C, E, A, D, B
Explanation
Sign in to read the full explanationQuestion 106
UGC NET November 2021Statement I: The Cleanroom software process model incorporates the statistical quality certification of code increments as they accumulate into a system.
Statement II: Cleanroom software engineering follows the classic analysis, design, code, test and debug cycle, focusing on defect removal rather than defect prevention.In light of the above statements, choose the correct answer from the options given below:
- ABoth Statement I and Statement II are true
- BBoth Statement I and Statement II are false
- CStatement I is true but Statement II is false
- DStatement I is false but Statement II is true
Answer: (C) Statement I is true but Statement II is false
Explanation
Sign in to read the full explanationQuestion 107
UGC NET November 2021Assertion (A): Software developers do not do exhaustive software testing in practice.
Reason (R): Even for small inputs, exhaustive testing is too computationally intensive (takes too long) to run all the tests.In light of the above statements, choose the correct answer from the options given below:
- ABoth A and R are true and R is the correct explanation of A
- BBoth A and R are true but R is NOT the correct explanation of A
- CA is true but R is false
- DA is false but R is true
Answer: (A) Both A and R are true and R is the correct explanation of A
Explanation
Sign in to read the full explanationQuestion 108
UGC NET November 2020Which UML diagram has a static view?
- ACollaboration diagram
- BUse-case diagram
- CState-chart diagram
- DActivity diagram
Answer: (B) Use-case diagram
Explanation
Sign in to read the full explanationQuestion 109
UGC NET November 2020Modifying software by restructuring is called
- AAdaptive maintenance
- BCorrective maintenance
- CPerfective maintenance
- DPreventive maintenance
Answer: (C) Perfective maintenance
Explanation
Sign in to read the full explanationQuestion 110
UGC NET November 2020A company can use languages L₁ and L₂; an application needs three times as many LOC in L₂ as in L₁. The project has 10 years of maintenance. For what LOC in L₁ are the total development-plus-maintenance costs equal?
Parameter L₁ L₂ Man-years for development LOC/1000 LOC/1000 Development cost Rs. 70,000 Rs. 90,000 Maintenance cost per year Rs. 1,00,000 Rs. 40,000 - A2000
- B6000
- C3000
- D5000
Answer: (C) 3000
Explanation
Sign in to read the full explanationQuestion 111
UGC NET November 2020A software project is estimated at 864 function points. A six-person team has one requirements gatherer (Rs. 50,000/month), one designer (Rs. 70,000/month), two programmers (Rs. 60,000/month each), and two testers (Rs. 60,000/month each). Team productivity is 12 FP per person-month. What is the projected cost?
- ARs. 33,20,000
- BRs. 43,20,000
- CRs. 33,10,000
- DRs. 22,10,000
Answer: (B) Rs. 43,20,000
Explanation
Sign in to read the full explanationQuestion 112
UGC NET November 2020Software reliability may be described with respect to
A. execution time,
B. calendar time, and
C. clock time.- A(A) and (B) only
- B(B) and (C) only
- C(A), (B), and (C)
- D(A) and (C) only
Answer: (C) (A), (B), and (C)
Explanation
Sign in to read the full explanationQuestion 113
UGC NET November 2020To create an object-behavioural model, an analyst
A. evaluates use cases,
B. builds a state-transition diagram,
C. reviews the model for accuracy and consistency, and
D. identifies events that do not drive an interaction sequence.- A(A), (B), and (C) only
- B(A), (B), and (D) only
- C(B), (C), and (D) only
- D(A), (C), and (D) only
Answer: (A) (A), (B), and (C) only
Explanation
Sign in to read the full explanationQuestion 114
UGC NET November 2020Which are behavioural (black-box) testing techniques?
A. Equivalence partitioning
B. Graph-based testing
C. Boundary-value analysis
D. Data-flow testing
E. Loop testing- A(B) and (D) only
- B(A), (B), and (C) only
- C(D) and (E) only
- D(A), (C), and (E) only
Answer: (B) (A), (B), and (C) only
Explanation
Sign in to read the full explanationQuestion 115
UGC NET November 2020Match List I with List IT
With reference to CMM developed by Software Engineering Institute (SEI)
List I List IT
A. INITIAL () Process measurement
B. REPEATABLE (Il) Process definition
C. DEFINED (ID Project management
D. MANAGED (Iv) ADHOCList I List II Items are listed in the question stem. Match each item to its stated description or complexity. - AAIT, B-IV, C-II. D-I
- BA-IV, B-IIl. C-I, D-II
- CA-IV, B-III, C-IL, D-I
- DALIII, B-IV, C-I, D-II
Answer: (C) A-IV, B-III, C-IL, D-I
Explanation
Sign in to read the full explanationQuestion 116
UGC NET November 2020Arrange the following types of Cohesion from best to worst type.
A. B. C. D. E. Logical Cohesion
Sequential Cohesion
Communication Cohesion
Temporal CohesionProcedural Cohesion
- AOCR review required
- BOCR review required
- COCR review required
- DOCR review required
Answer: (D) OCR review required
Explanation
Sign in to read the full explanationQuestion 117
UGC NET November 2020Given below are two statements:
Statement I: Quality control involves the series of inspections. reviews and tests used
throughout the software process, to ensure each work product meets the
requirements placed upon it.Statement II: Quality assurance consists of auditing and reporting functions of
management.
In the light of the above statements, choose the correct answer from the options given below
qd)
- AOCR review required
- BOCR review required
- COCR review required
- DOCR review required
Answer: (A) OCR review required
Explanation
Sign in to read the full explanationQuestion 118
UGC NET December 2019According to the ISO-9126 Standard Quality Model, match the attributes in List-I with their definitions in List-II.
List-I List-II (a) Functionality (i) Relationship between level of performance and amount of resources (b) Reliability (ii) Characteristics related with achievement of purpose (c) Efficiency (iii) Effort needed to make for improvement (d) Maintainability (iv) Capability of software to maintain performance of software - A(a)-(i), (b)-(ii), (c)-(iii), (d)-(iv)
- B(a)-(ii), (b)-(i), (c)-(iv), (d)-(iii)
- C(a)-(ii), (b)-(iv), (c)-(i), (d)-(iii)
- D(a)-(i), (b)-(ii), (c)-(iv), (d)-(iii)
Answer: (C) (a)-(ii), (b)-(iv), (c)-(i), (d)-(iii)
Explanation
Sign in to read the full explanationQuestion 119
UGC NET December 2019Match the Agile Process models with the task performed during the model.
List-I List-II (a) Scrum (i) CRC cards (b) Adaptive software development (ii) Sprint backlog (c) Extreme programming (iii) <action> the <result> <by/for/of/to> a(n) <object> (d) Feature-driven development (iv) Time box release plan - A(a)-(ii), (b)-(iv), (c)-(i), (d)-(iii)
- B(a)-(i), (b)-(ii), (c)-(iii), (d)-(iv)
- C(a)-(ii), (b)-(i), (c)-(iv), (d)-(iii)
- D(a)-(i), (b)-(iv), (c)-(ii), (d)-(iii)
Answer: (A) (a)-(ii), (b)-(iv), (c)-(i), (d)-(iii)
Explanation
Sign in to read the full explanationQuestion 120
UGC NET December 2019The sequence diagram for the Weather Information System takes place when an external system requests the summarized data from the weather station. The increasing order of lifeline for the objects in the system are:
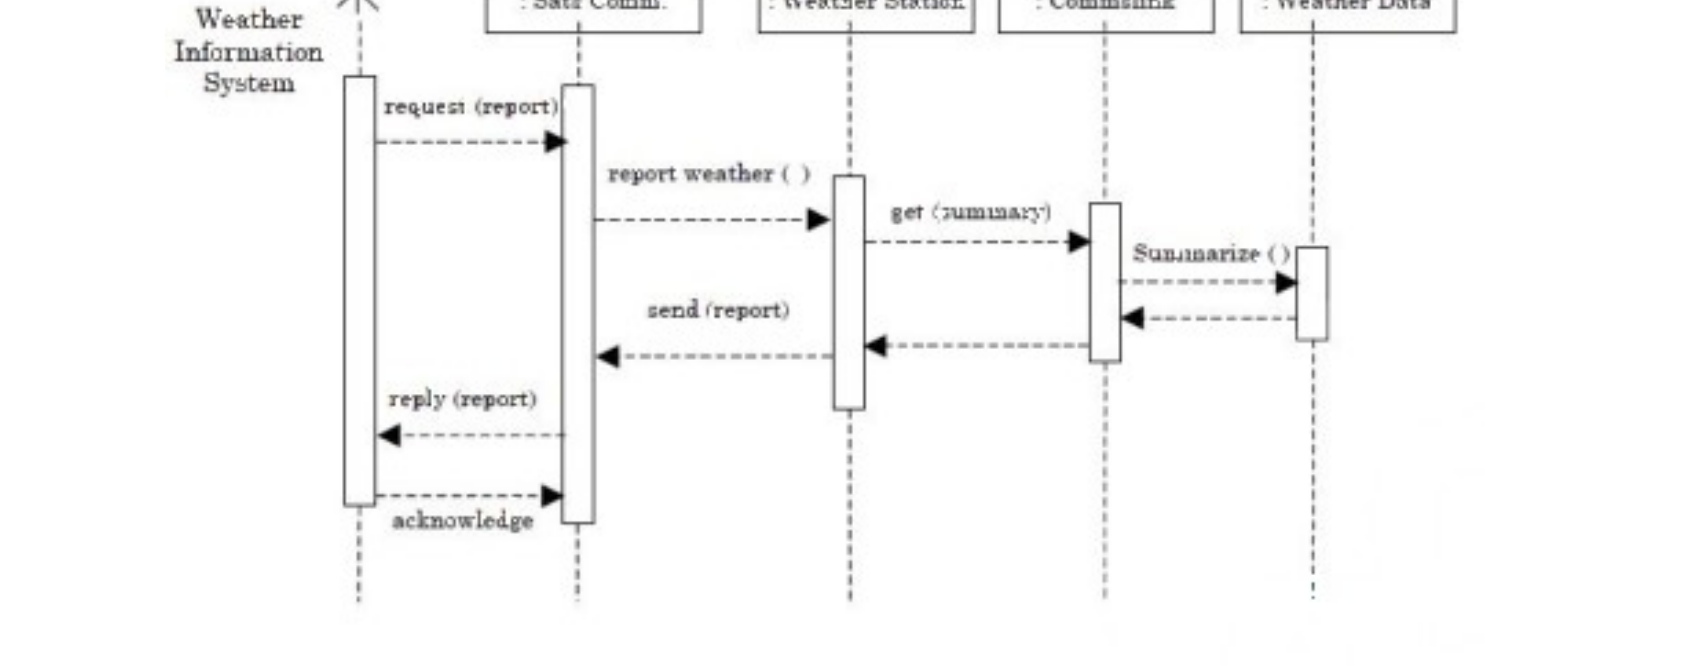
UML sequence diagram for the Weather Information System
- ASat comms → Weather station → Comms link → Weather data
- BSat comms → Comms link → Weather station → Weather data
- CWeather data → Comms link → Weather station → Sat Comms
- DWeather data → Weather station → Comms link → Sat Comms
Accepted answers: (C) Weather data → Comms link → Weather station → Sat Comms, (D) Weather data → Weather station → Comms link → Sat Comms
Explanation
Sign in to read the full explanationQuestion 121
UGC NET December 2019An activity chart is a project schedule representation that presents project plan as a directed graph. The critical path is the __________ sequence of __________ tasks and it defines project __________.
- AActivity, Shortest, Independent, Cost
- BActivity, Longest, Dependent, Duration
- CActivity, Longest, Independent, Duration
- DActivity, Shortest, Dependent, Duration
Answer: (B) Activity, Longest, Dependent, Duration
Explanation
Sign in to read the full explanationQuestion 122
UGC NET December 2019In a system for a restaurant, the main scenario for placing order is given below:
(a) Customer reads menu
(b) Customer places order
(c) Order is sent to kitchen for preparation
(d) Ordered items are served
(e) Customer requests for a bill for the order
(f) Bill is prepared for this order
(g) Customer is given the bill
(h) Customer pays the billA sequence diagram for the scenario will have atleast how many objects among whom the messages will be exchanged?
- A3
- B4
- C5
- D6
Answer: (C) 5
Explanation
Sign in to read the full explanationQuestion 123
UGC NET December 2019Answer the question based on flow graph F with entry node (1) and exit node (11).
How many regions are there in flowgraph F?
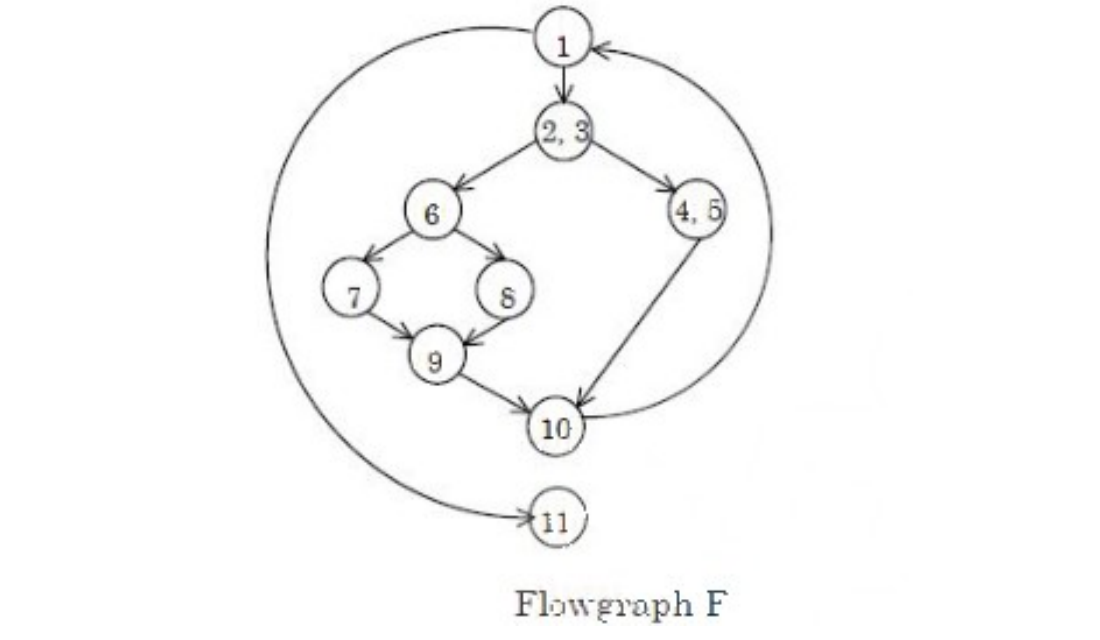
Flowgraph F control flow diagram
- A2
- B3
- C4
- D5
Answer: (C) 4
Explanation
Sign in to read the full explanationQuestion 124
UGC NET December 2019Answer the question based on flow graph F with entry node (1) and exit node (11).
How many nodes are there in the longest independent path?
Flowgraph F control flow diagram
- A6
- B7
- C8
- D9
Answer: (C) 8
Explanation
Sign in to read the full explanationQuestion 125
UGC NET December 2019Answer the question based on flow graph F with entry node (1) and exit node (11).
How many predicate nodes are there and what are their names?
Flowgraph F control flow diagram
- AThree : (1, (2, 3), 6)
- BThree : (1, 4, 6)
- CFour : ((2, 3), 6, 10, 11)
- DFour : ((2, 3), 6, 9, 10)
Answer: (A) Three : (1, (2, 3), 6)
Explanation
Sign in to read the full explanation- Practise Software Engineering in a timed set
Question 126
UGC NET December 2019Answer the question based on flow graph F with entry node (1) and exit node (11).
What is the cyclomatic complexity of flowgraph F?
Flowgraph F control flow diagram
- A2
- B3
- C4
- D5
Answer: (C) 4
Explanation
Sign in to read the full explanationQuestion 127
UGC NET December 2019Answer the question based on flow graph F with entry node (1) and exit node (11).
How many nodes are there in flowgraph F?
Flowgraph F control flow diagram
- A9
- B10
- C11
- D12
Answer: (A) 9
Explanation
Sign in to read the full explanationQuestion 128
UGC NET June 2019Software products need adaptive maintenance for which of the following reasons?
- ATo rectify bugs observed while the system is in use
- BWhen the customers need the product to run on new platforms
- CTo support the new features that users want it to support
- DTo overcome wear and tear caused by the repeated use of the software
Answer: (B) When the customers need the product to run on new platforms
Explanation
Sign in to read the full explanationQuestion 129
UGC NET June 2019In the context of software testing, which of the following statements is/are NOT correct?
P: A minimal test set that achieves 100% path coverage will also achieve 100% statement coverage.
Q: A minimal test set that achieves 100% path coverage will generally detect more faults than one that achieves 100% statement coverage.
R: A minimal test set that achieves 100% statement coverage will generally detect more faults than one that achieves 100% branch coverage.- AR only
- BQ only
- CP and Q only
- DQ and R only
Answer: (A) R only
Explanation
Sign in to read the full explanationQuestion 130
UGC NET June 2019Which of the following are the primary objectives of risk monitoring in software project tracking?
P: To assess whether predicted risks do, in fact, occur
Q: To ensure that risk aversion steps defined for the risk are being properly applied
R: To collect information that can be used for future risk analysis- AOnly P and Q
- BOnly P and R
- COnly Q and R
- DAll of P, Q, R
Answer: (D) All of P, Q, R
Explanation
Sign in to read the full explanationQuestion 131
UGC NET June 2019The M components in MVC are responsible for
- Auser interface
- Bsecurity of the system
- Cbusiness logic and domain objects
- Dtranslating between user interface actions/events and operations on the domain objects
Answer: (C) business logic and domain objects
Explanation
Sign in to read the full explanationQuestion 132
UGC NET June 2019Which of the following statements is/are true?
P: In software engineering, defects that are discovered earlier are more expensive to fix.
Q: A software design is said to be a good design, if the components are strongly cohesive and weakly coupled.Select the correct answer from the options given below:
- AP only
- BQ only
- CP and Q
- DNeither P nor Q
Answer: (B) Q only
Explanation
Sign in to read the full explanationQuestion 133
UGC NET June 2019Software validation mainly checks for inconsistencies between
- Ause cases and user requirements
- Bimplementation and system design blueprints
- Cdetailed specifications and user requirements
- Dfunctional specifications and use cases
Answer: (C) detailed specifications and user requirements
Explanation
Sign in to read the full explanationQuestion 134
UGC NET June 2019Match List-I with List-II:
List-I (Software Process Models)
(a) Waterfall model
(b) Incremental development
(c) Prototyping
(d) RAD
List-II (Software Systems)
(i) e-business software that starts with only the basic functionalities and then moves on to more advanced features
(ii) An inventory control system for a super-market to be developed within three months
(iii) A virtual reality system for simulating vehicle navigation in a highway
(iv) Automate the manual system for student record maintenance in a schoolList-I (Software Process Models) List-II (Software Systems) (a) Waterfall model (iv) Automate the manual system for student record maintenance in a school (b) Incremental development (i) e-business software that starts with only the basic functionalities and then moves on to more advanced features (c) Prototyping (iii) A virtual reality system for simulating vehicle navigation in a highway (d) RAD (ii) An inventory control system for a super-market to be developed within three months - A(a)-(ii); (b)-(iv); (c)-(i); (d)-(iii)
- B(a)-(i); (b)-(iii); (c)-(iv); (d)-(ii)
- C(a)-(iii); (b)-(ii); (c)-(iv); (d)-(i)
- D(a)-(iv); (b)-(i); (c)-(iii); (d)-(ii)
Answer: (D) (a)-(iv); (b)-(i); (c)-(iii); (d)-(ii)
Explanation
Sign in to read the full explanationQuestion 135
UGC NET June 2019Software reuse is
- Athe process of analysing software with the objective of recovering its design and specification
- Bthe process of using existing software artifacts and knowledge to build new software
- Cconcerned with reimplementing legacy system to make them more maintainable
- Dthe process of analysing software to create a representation of a higher level of abstraction and breaking software down into its parts to see how it works
Answer: (B) the process of using existing software artifacts and knowledge to build new software
Explanation
Sign in to read the full explanationQuestion 136
UGC NET June 2019A Web application and its support environment has not been fully fortified against attack. Web engineers estimate that the likelihood of repelling an attack is only 30 percent. The application does not contain sensitive or controversial information, so the threat probability is 25 percent. What is the integrity of the web application?
- A0.625
- B0.725
- C0.775
- D0.825
Answer: (D) 0.825
Explanation
Sign in to read the full explanationQuestion 137
UGC NET June 2019Which of the following terms best describes Git?
- AIssue Tracking System
- BIntegrated Development Environment
- CDistributed Version Control System
- DWeb-based Repository Hosting Service
Answer: (C) Distributed Version Control System
Explanation
Sign in to read the full explanationQuestion 138
UGC NET December 2018Which of the following is not one of the principles of agile software development method ?
- AEmbrace change
- BCustomer involvement
- CFollowing the plan
- DIncremental delivery
Answer: (C) Following the plan
Explanation
Sign in to read the full explanationQuestion 139
UGC NET December 2018Software coupling involves dependencies among pieces of software called modules. Which of the following are correct statements with respect to module coupling ?
P : Common coupling occurs when two modules share the same global data.
Q : Control coupling occurs when modules share a composite data structure and use only parts of it.
R : Content coupling occurs when one module modifies or relies on the internal working of another module.Choose the correct answer from the code given below :
Code :- AP and Q only
- BQ and R only
- CAll of P, Q and R
- DP and R only
Answer: (D) P and R only
Explanation
Sign in to read the full explanationQuestion 140
UGC NET December 2018Software products need perfective maintenance for which of the following reasons ?
- ATo overcome wear and tear caused by the repeated use of the software.
- BTo rectify bugs observed while the system is in use.
- CWhen the customers need the product to run on new platforms.
- DTo support the new features that users want it to support.
Answer: (D) To support the new features that users want it to support.
Explanation
Sign in to read the full explanationQuestion 141
UGC NET December 2018Which of the following statements is/are true ?
P : Software Reengineering is preferable for software products having high failure rates, having poor design and/or having poor code structure.
Q : Software Reverse Engineering is the process of analyzing software with the objective of recovering its design and requirements specification.Choose the correct answer from the code given below :
Code :- ABoth P and Q
- BNeither P nor Q
- CP only
- DQ only
Answer: (A) Both P and Q
Explanation
Sign in to read the full explanationQuestion 142
UGC NET December 2018Which of the following statements is/are false ?
P : The clean-room strategy to software engineering is based on the incremental software process model.
Q : The clean-room strategy to software engineering is one of the ways to overcome “unconscious” copying of copyrighted code.Choose the correct answer from the code given below :
Code :- ANeither P nor Q
- BQ only
- CBoth P and Q
- DP only
Answer: (A) Neither P nor Q
Explanation
Sign in to read the full explanationQuestion 143
UGC NET December 2018Match each UML diagram in List-I to its appropriate description in List-II and choose the correct answer from the code:
List-I List-II (a) State Diagram (i) Describes how the external entities (people, devices) can interact with the system. (b) Use-Case Diagram (ii) Used to describe the static or structural view of a system. (c) Class Diagram (iii) Used to show the flow of a business process, the steps of a use-case or the logic of an object behaviour. (d) Activity Diagram (iv) to the dynamic behaviour of objects and could also be used to describe the entire system behaviour. UML diagrams and descriptions
- A(iv) (ii) (i) (iii)
- B(iv) (i) (ii) (iii)
- C(i) (iv) (iii) (ii)
- D(i) (iv) (ii) (iii)
Answer: (B) (iv) (i) (ii) (iii)
Explanation
Sign in to read the full explanationQuestion 144
UGC NET December 2018The Software Requirement Specification (SRS) is said to be ___________ if and only if no subset of individual requirements described in it conflict with each other.
- AConsistent
- BUnambiguous
- CCorrect
- DVerifiable
Answer: (A) Consistent
Explanation
Sign in to read the full explanationQuestion 145
UGC NET December 2018Consider the following method :
int f (int m, int n, boolean x, boolean y)
{
 int res = 0;
 if (m < 0) {res = n – m;}
 else if (x || y) {
 res = –1;
 if (n == m) {res = 1;}
 }
 else {res = n;}
 return res;
}/* end of */
If P is the minimum number of tests to achieve full statement coverage for f(), and Q is the minimum number of tests to achieve full branch coverage for f(), then (P, Q) =
- A(3, 2)
- B(2, 3)
- C(4, 3)
- D(3, 4)
Answer: (D) (3, 4)
Explanation
Sign in to read the full explanationQuestion 146
UGC NET December 2018A legacy software system has 940 modules. The latest release required that 90 of these modules be changed. In addition, 40 new modules were added and 12 old modules were removed. Compute the software maturity index for the system.
- A0·849
- B0·923
- C0·725
- D0·524
Answer: (A) 0·849
Explanation
Sign in to read the full explanation
Frequently asked questions
How many Software Engineering questions have been asked in UGC NET Computer Science?
146 Software Engineering questions appear in the UGC NET Computer Science papers held between 2018–2026, and all of them are on this page with their answer key.
Are the answers on this page free?
Yes. Every question, its options, and the correct answer are free to read with no account. Signing in additionally unlocks the detailed explanation under each question.
Is Software Engineering an important topic for UGC NET Computer Science?
Software Engineering appears in every recent UGC NET Computer Science paper, across all 14 sittings covered here. Its share of the paper makes it worth revising thoroughly rather than sampling.
How should I practise Software Engineering after reading these questions?
Attempt the Software Engineering topic-wise sets, which put the same questions into a timed interface with instant scoring and weak-area analysis afterwards.
More Computer Science PYQs by topic
More Computer Science practice
Ready for a full paper?
Attempt Paper 1 + Paper 2 (Computer Science) together in a single timed session.